Managing Cybersecurity Risk in Modern MSP Environments
Managing Cybersecurity Risk in Modern MSP Environments
“We are a revenue protector. If you go down due to this, think about how many thousands of dollars every minute you are losing.”
Who They Brought In
For managed service providers (MSPs) and managed security service providers (MSSPs), cybersecurity is no longer just about technical support. Organizations must balance MSP compliance and cybersecurity risk management requirements, asset inventory management, patch management, and cybersecurity risk management while protecting revenue from costly downtime. In this episode, AXE Computers USA President Kevin Neureuter Jr. shares his approach to compliance, security operations, risk tolerance, and why visibility into every device on the network remains the foundation of effective cybersecurity.
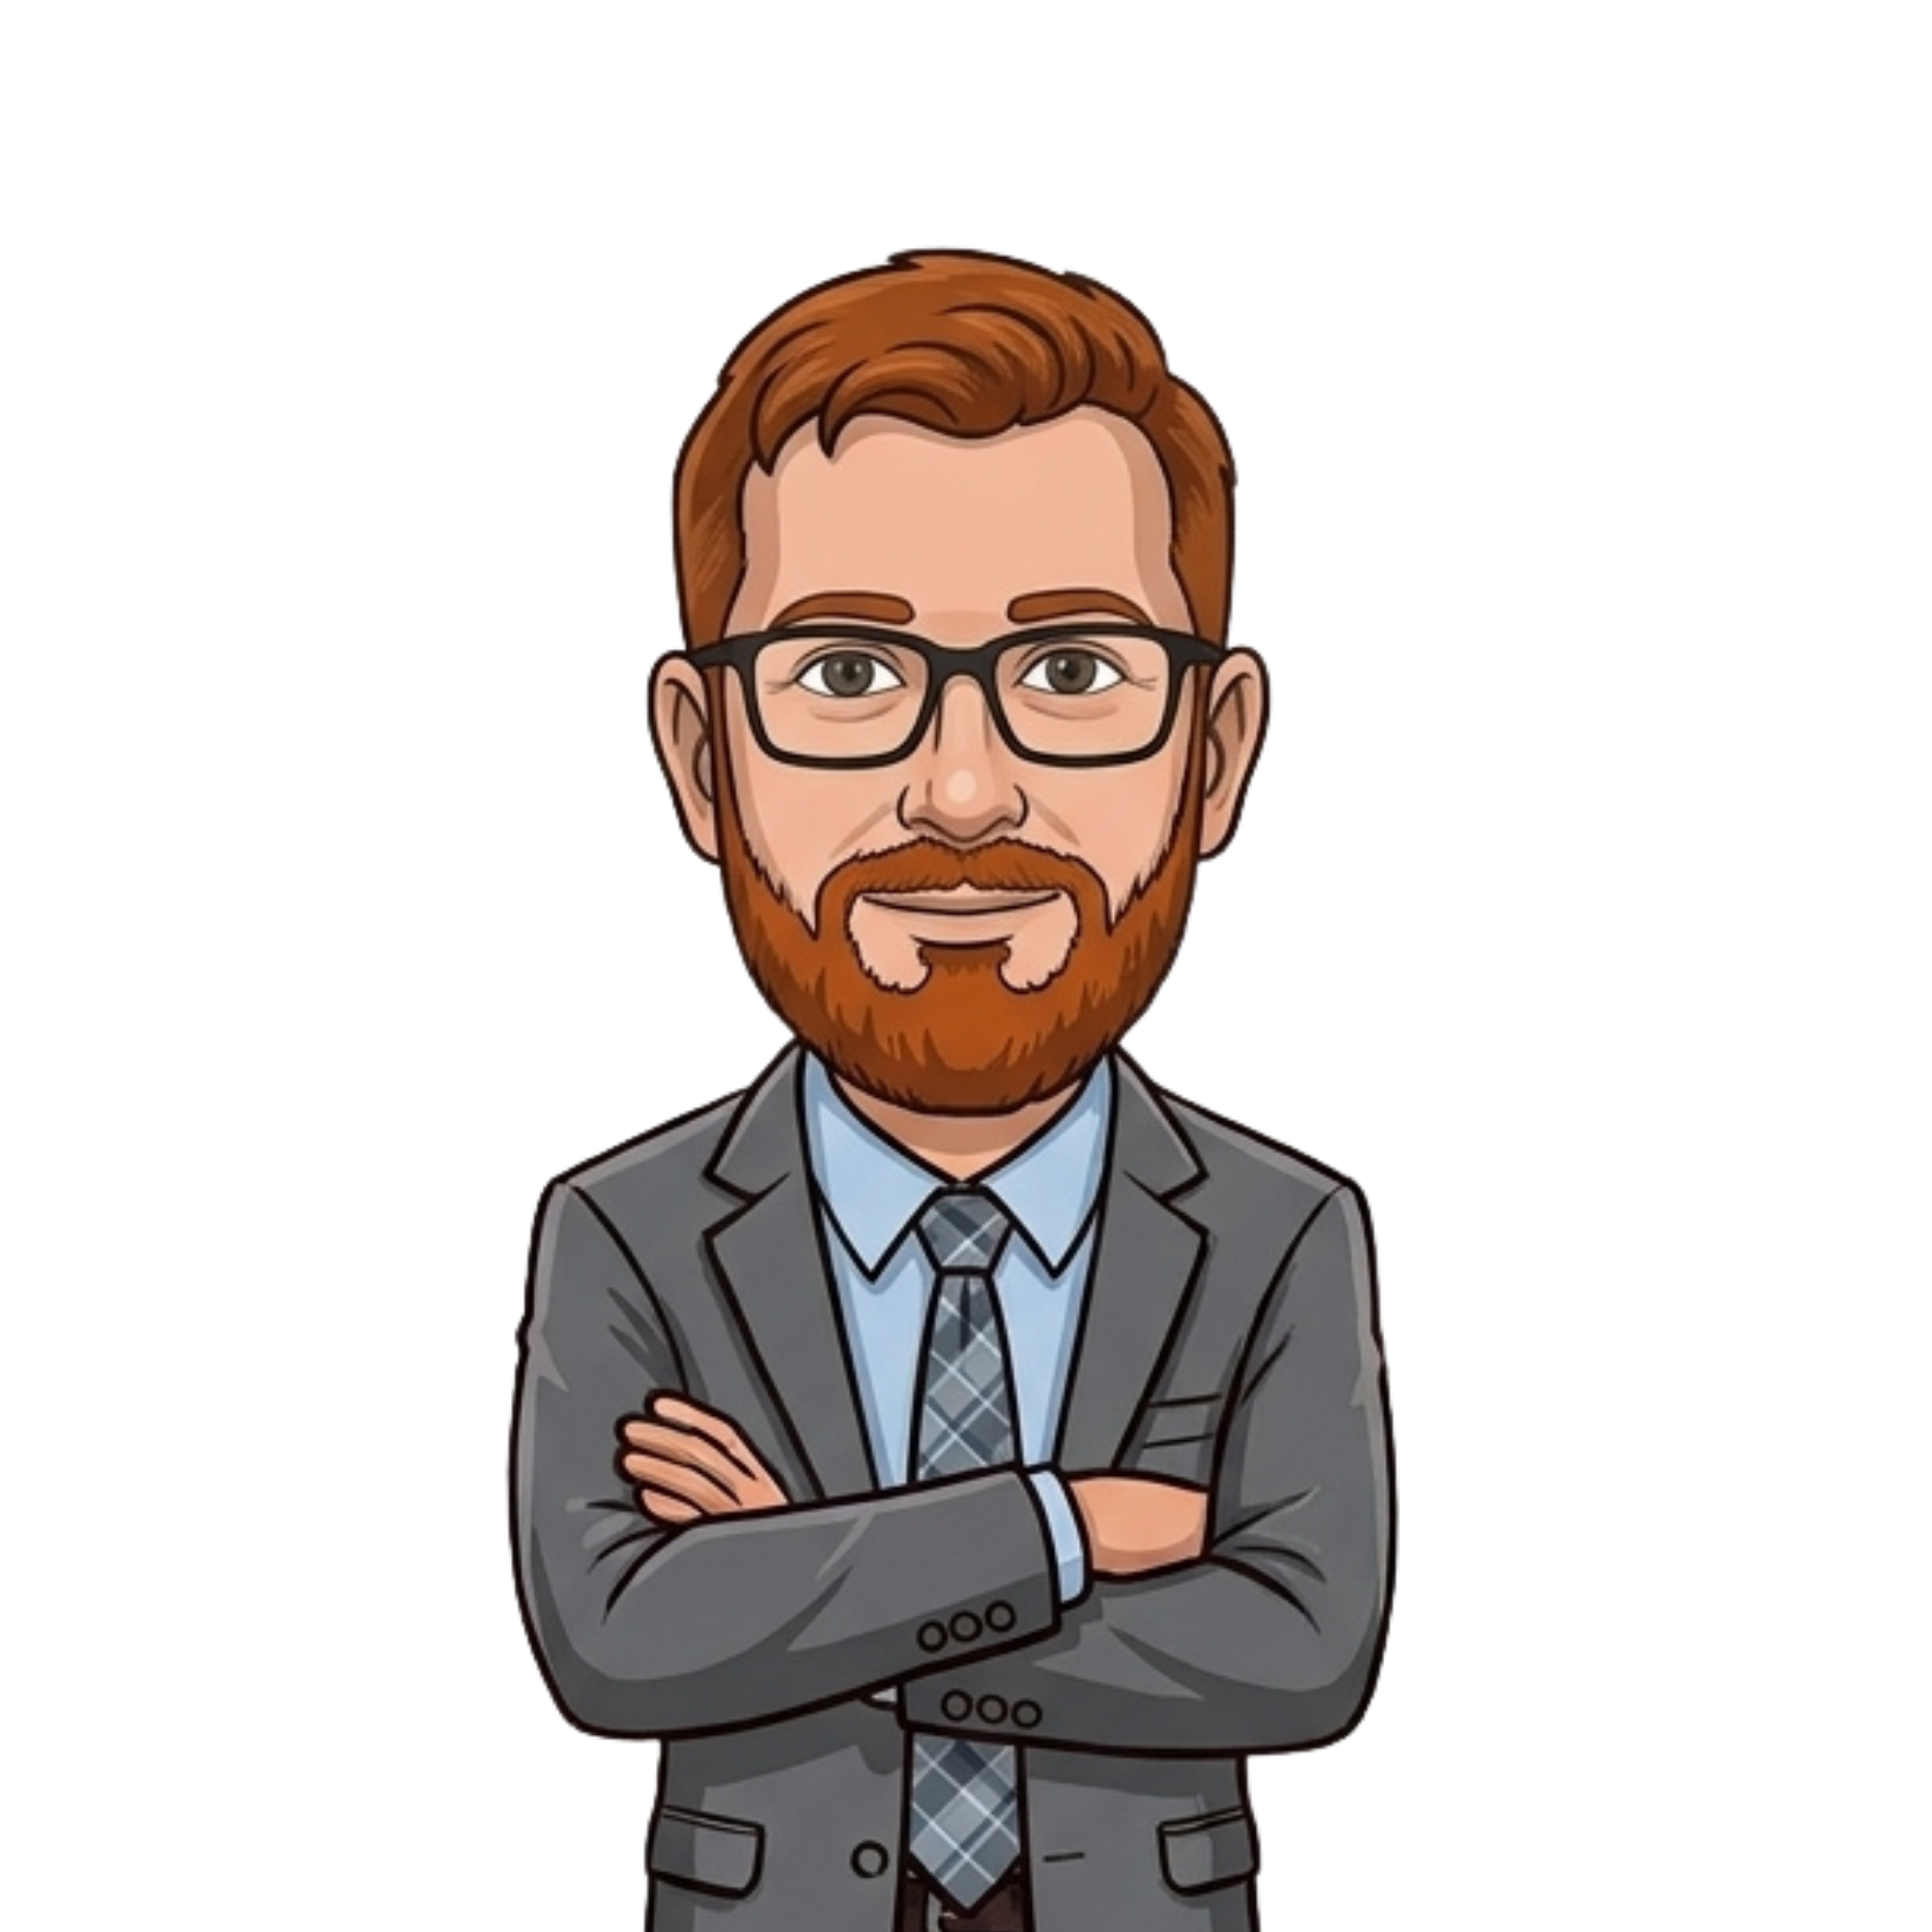
Kevin Neureuter, Jr. is the President and Owner of AXE Computers USA, an MSSP he has run for 12 years, operating alongside his wife, who is a 50 percent owner of the business. Kevin spent 17 years in federal contracting and logistics before an unexpected opening pulled him into IT, and he later served as Director of IT for Orleans County, New York, before building AXE Computers into a company focused on compliance, hardware inventory discipline, and federal contracting support.
What Got Loud
- Kevin’s business philosophy in one line: an IT function is not a cost center, it is a revenue protector, and every minute of downtime has a real dollar cost attached to it.
- His biggest, most overlooked compliance gap: companies have no idea what hardware is actually sitting on their network, sometimes hundreds of thousands of dollars worth of it.
- His hard line with customers: patching is non-negotiable and part of the package, even when a prospect pushes back.
- His read on AI tools like Copilot: an 80 percent solution for policy writing and proposal drafting, but a human always has to tweak the last 20 percent for that specific company.
- His read on risk appetite: some MSPs will not take a customer who refuses baseline security, others will, and both can build a profitable business, just with very different books.
The Rundown
Kevin runs AXE Computers USA the way he says every good MSP should, by starting with customer service rather than sales. He and his wife describe themselves as stewards rather than owners of the business, a mindset Kevin credits to something he heard from the owner of Hobby Lobby and adopted for his own company. His path into IT was not planned. He was working in logistics and supply chain for a federal contractor when the vice president and program manager both died the same year, leaving the organization without anyone managing its technology. As the youngest person in the office and the only one comfortable with computers, Kevin was handed the job. He rebuilt the company’s IT from pirated software and Windows XP machines, and that experience, plus a home repair project on an old Dell laptop, became the start of his business.
Hardware inventory and network asset discovery are where Kevin’s compliance and cybersecurity programs begin. He argues that many organizations struggle with asset management because they lack accurate inventories of the devices connected to their environments, creating security, compliance, and operational risks.
“They only know what they tell you, right? There could be a bunch somewhere else, or they’re using something that you’re unaware of because you just don’t know, and they don’t know either.”
He walked through examples from his own client visits, including a warehouse where he found laptops nobody on site knew existed, and a building where an employee of 20 years insisted there was no window in a room until Kevin asked them to go look again. His approach is to physically walk the site rather than rely on what a customer reports, a habit he traces back to military property accountability, where he had to personally verify every asset at least once a year.
On patch management, Kevin draws a clear line. While he is willing to customize security recommendations around a client’s budget and risk tolerance, maintaining current software updates remains non-negotiable. Effective patch management continues to be one of the most important cybersecurity controls for reducing organizational risk and maintaining compliance requirements. MSP compliance and cybersecurity risk management. He will build a custom solution around a client’s budget and risk tolerance in almost every other area, but patching stays non-negotiable because the business carries risk along with the customer when something goes wrong. He contrasted his own middle-ground risk appetite with two of his peers: one who refuses any customer that will not commit to MFA, SIEM, and SOC coverage, and another who still struggles to get basic patching approved. Kevin sees both as viable businesses with different pricing and different risk profiles, not one right answer.
On AI, Kevin uses Microsoft Copilot for policy writing, proposal drafting, and business decision support, but is clear about its limitations. He views AI as a valuable productivity tool for cybersecurity documentation and compliance workflows, while emphasizing that security policies must still be reviewed and customized by experienced professionals.
“I find that it’s an 80 percent solution, but that human needs to be in there to tweak it and get the nuance type of things that it won’t fit or it won’t work. That’s where I come in, that 20 percent.”
He described reviewing AI-written security policies from other companies and testing them by asking specific follow-up questions, often finding the policy referenced tools or controls the business did not actually have in place. For Kevin, every policy still has to be rebuilt around the specific company, because no two clients run the same environment or face the same risk.
The challenge highlights a growing concern in cybersecurity compliance: organizations increasingly rely on AI-generated content without validating whether documented security controls actually exist. For MSPs and MSSPs, policy management remains a critical component of security governance and audit readiness.
Real Talk
Kevin’s framing of IT as a revenue protector rather than a cost center is a useful reframe for any MSP compliance and cybersecurity risk management experts trying to get budget approved by a business owner instead of an IT director. But the sharper point in this conversation is his insistence on physically verifying what is actually on a network before trusting any report of what is supposed to be there.
Catch It
Watch the full conversation with Kevin Neureuter, Jr. on SOCSoter Unfiltered for more on hardware inventory discipline, federal contracting and property management as MSP verticals, and where AI is actually earning its place in day-to-day IT operations. Visit socsoter.com